Active Directory changes such as user account modifications, group membership changes, computer account changes, and changes to directory objects can be recorded in the Security logs on domain controllers when the appropriate auditing is configured.
You can use Windows Event Viewer to find these events and determine who made a change, what object was affected, when the change occurred, and, for certain directory service changes, which attribute was modified.
This guide explains how to track Active Directory changes using Event Viewer and relevant Windows Security event IDs, including Directory Service Changes events (5136–5141) and Account Management events (47xx).
Prerequisites
Before tracking Active Directory changes, make sure:
- The appropriate Advanced Audit Policy settings are enabled on your domain controllers.
- You have permission to access the Security logs on your domain controllers.
- Appropriate object-level auditing (SACLs) is configured where required for Directory Service Changes events.
Enable Auditing Before Tracking Active Directory Changes
Before Windows can record the required Active Directory changes, the appropriate Advanced Audit Policy settings must be enabled on your domain controllers.
In Group Policy Management, these settings are available under:
Computer Configuration → Policies → Windows Settings → Security Settings → Advanced Audit Policy Configuration → Audit Policies
For tracking common Active Directory changes, relevant audit subcategories include:
- Audit Directory Service Changes – records changes to Active Directory objects.
- Audit User Account Management – records user account management activities.
- Audit Security Group Management – records changes to security groups and their membership.
- Audit Computer Account Management – records computer account management activities.
Detailed Directory Service Changes events may also depend on appropriate object-level auditing entries (SACLs) being configured for the objects or containers you want to monitor.
For complete step-by-step instructions on configuring these audit policies and object-level auditing, see How to Enable Active Directory Auditing.
How to Review Active Directory Audit Logs in Event Viewer
After configuring the required audit policies and object auditing, you can review Active Directory changes in the Security log on a domain controller.
- Open Server Manager → Tools → Event Viewer.
- Navigate to Windows Logs → Security.
- Click Filter Current Log in the Actions pane.
- In the <All Event IDs> field, enter the event IDs for the types of Active Directory changes you want to investigate.
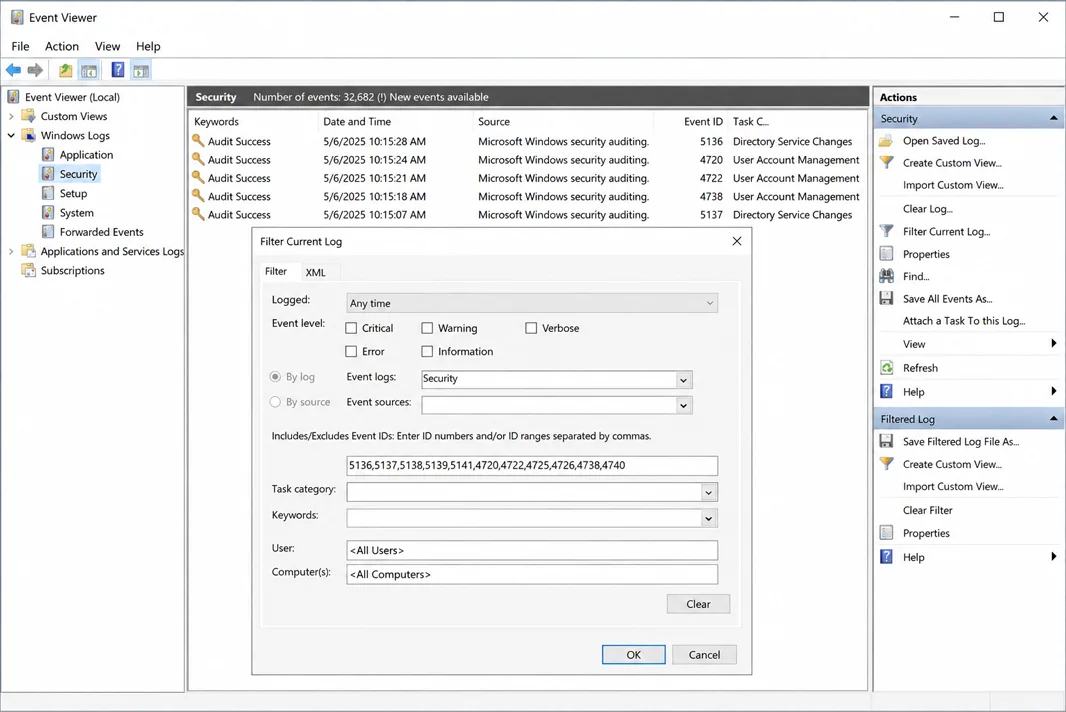
Directory Service Changes
User Account Changes
Security Group Membership Changes
- Click OK to display the matching events.
- Open an event and review its details to determine who performed the action, which account or Active Directory object was affected, when the change occurred, and other information associated with the event.
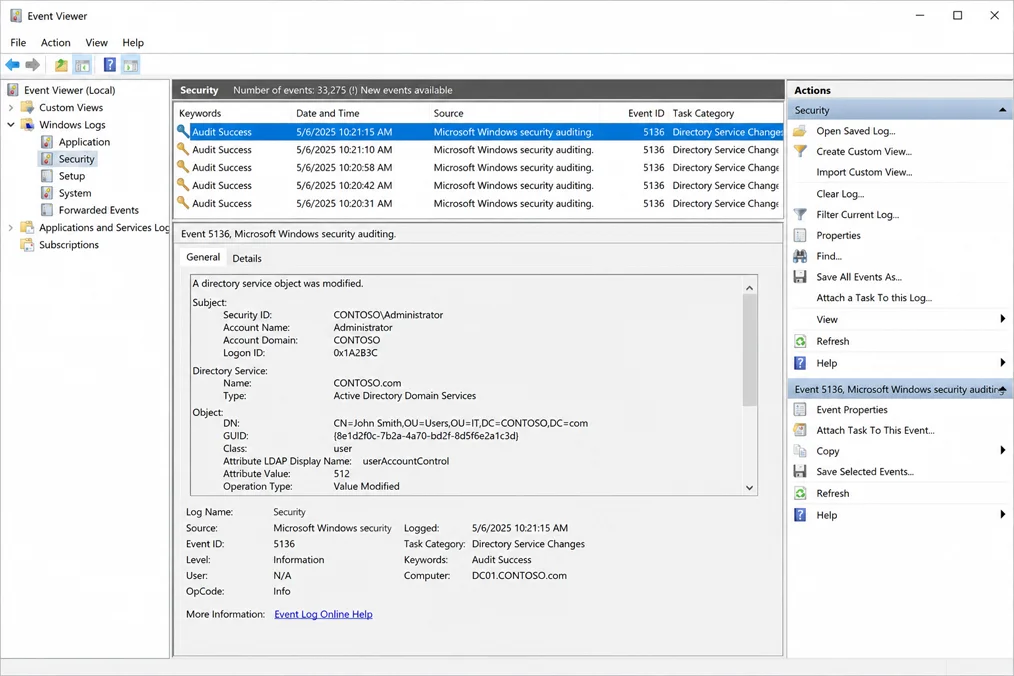
For Event ID 5136, review fields such as Subject, Object, Attribute LDAP Display Name, Attribute Value, and Operation Type. An attribute modification can generate separate events showing Value Deleted for the previous value and Value Added for the new value.
How Lepide Active Directory Auditor Tracks Changes Made in AD
For many users, manual auditing can be both time-consuming and unreliable, as you have to search lots of audit logs in the Event Viewer; it does not generate instant alerts and reports for Active Directory changes.
It is therefore recommended that you opt for an automated Active Directory auditing solution. One such solution is Lepide Active Directory Auditor, which enables users to pro-actively track, alert and report on changes being made to Active Directory.
Lepide’s Active Directory audit solution for records the details of every change made in the configuration of Active Directory and generates 90 reports in three different categories – Active Directory Modification Reports, Active Directory Security Reports, and Active Directory State Reports.
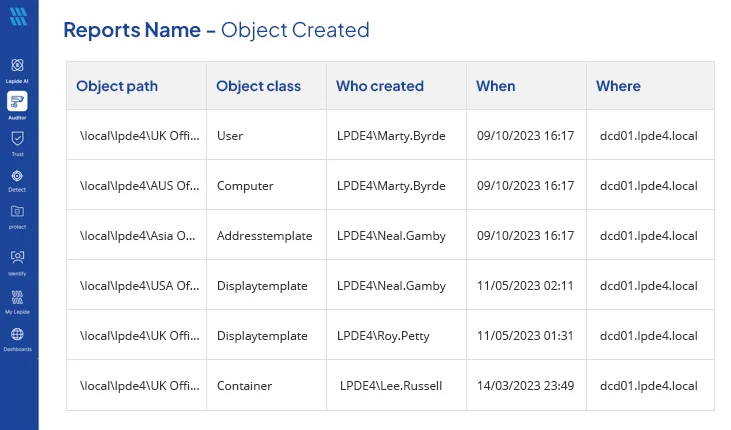
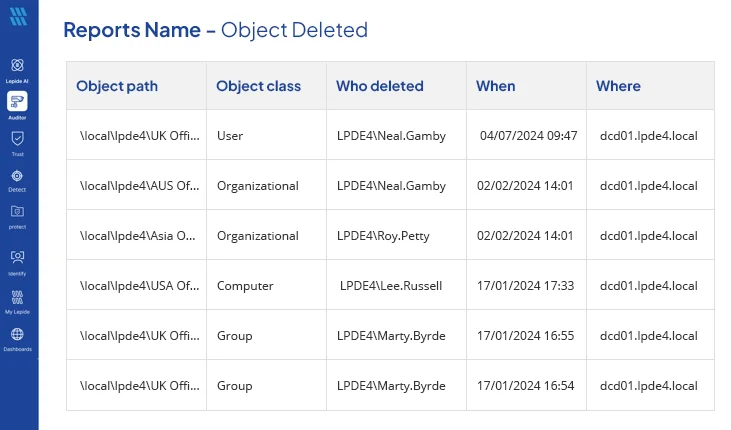
Below are some screenshots that show how our Active Directory auditing solution helps IT administrators track changes in Active Directory objects. Three reports are shown below; a report for objects created, objects deleted and objects modified.
- Object Created Report
- Object Deleted Report
- Object Modifications Report
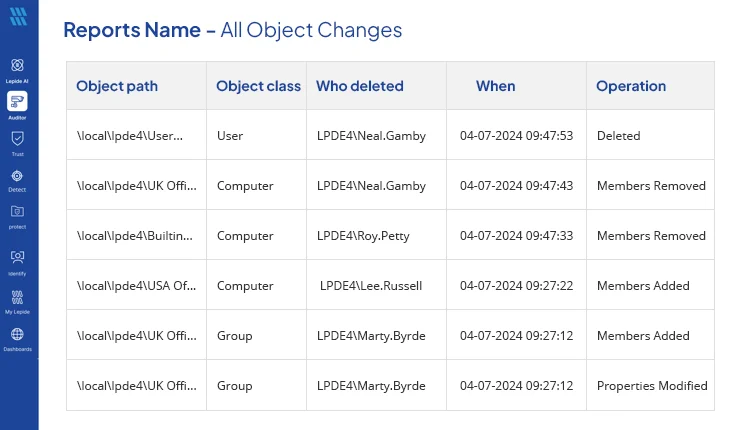
You can also track other activities like successful and failed logon attempts, account lockouts, permissions changes, privilege user activities etc. easily with our solution.
The Final Note
Lepide Active Directory Auditor for can actually make the whole Active Directory auditing process simpler through its intuitive user interface and sending real-time alerts as emails to desired recipients, as updates to LiveFeed widget, and as push-notifications to Lepide Mobile App to ensure the security of your Active Directory environment.