An Active Directory account lockout occurs when failed authentication attempts reach the account lockout threshold configured in the applicable account lockout policy. The account remains locked until it is automatically unlocked after the configured duration or manually unlocked by an administrator, depending on the policy.
Quick Reference: Key Event IDs
Why Does an AD Account Get Locked Out Frequently?
Below are some of the common causes of frequent AD account lockouts:
- Cached Credentials – Outdated passwords stored in Windows Credential Manager or other applications that repeatedly attempt authentication against Active Directory.
- Service Accounts – Windows services configured with a user account that has an expired or changed password
- Scheduled Tasks – Automated tasks running with saved credentials that no longer match the current password
- Mobile Devices – Smartphones or tablets with saved Exchange/email credentials attempting to sync with old passwords
- Terminal Service Sessions – Disconnected RDP sessions that remain active with stale credentials
- Password Changes – Passwords changed in Active Directory but not updated in applications, services, or devices that continue attempting authentication with old credentials.
- Misconfigured Applications – Applications or authentication integrations repeatedly submitting invalid credentials, potentially triggering account lockouts.
- Brute-Force Attacks – Malicious attempts to guess passwords by systematically trying multiple combinations
Read more about common account lockout causes in detail.
Prerequisites
Before starting the troubleshooting process, ensure you have:
- An account with permission to read the Security event logs on the relevant domain controllers
- Access to Event Viewer on the domain controllers
- Advanced Audit Policy Configuration → Account Management → Audit User Account Management enabled for Success auditing on the domain controllers
How to Find Out the AD Account Lockout Source?
If you already know which account is locked out, you can use its name to locate the relevant Event ID 4740 after completing Steps 1–3.
Step 1: Identify the PDC Emulator
The domain controller holding the PDC Emulator role is the recommended starting point for investigating account lockouts using Event ID 4740. If the expected event is unavailable, check the Security logs on other domain controllers that may have processed the lockout.
To identify the PDC Emulator, run the following PowerShell command:
Get-ADDomain | Select-Object PDCEmulatorStep 2: Open the Security Logs
On the identified domain controller, open Event Viewer and navigate to Windows Logs → Security.
Step 3: Search for Event ID 4740
In Event Viewer, select Filter Current Log, enter 4740 in the Event IDs field, and click OK.
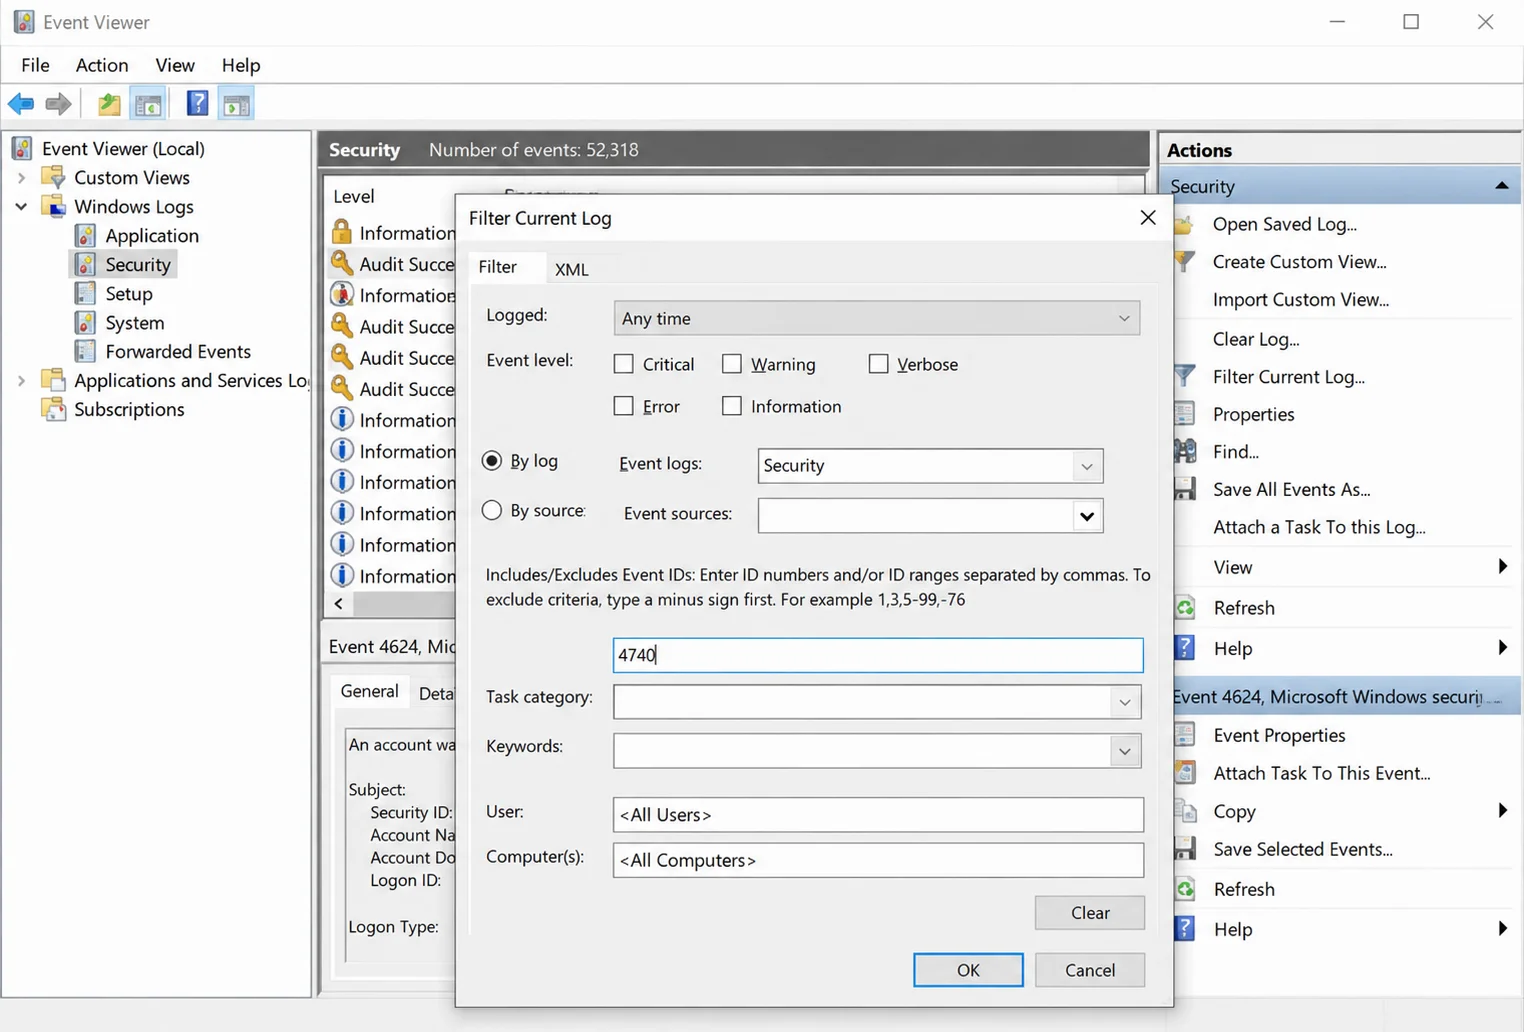
You can also specify a time range, such as the last hour, to narrow the results.
Step 4: Find Out the Locked Account Whose Information is Required
Use the Find option in Event Viewer to search for the account name associated with the lockout.
Step 5: Identify the Account Lockout Source
Open the relevant Event ID 4740 and review the Account That Was Locked Out section to identify the affected user.
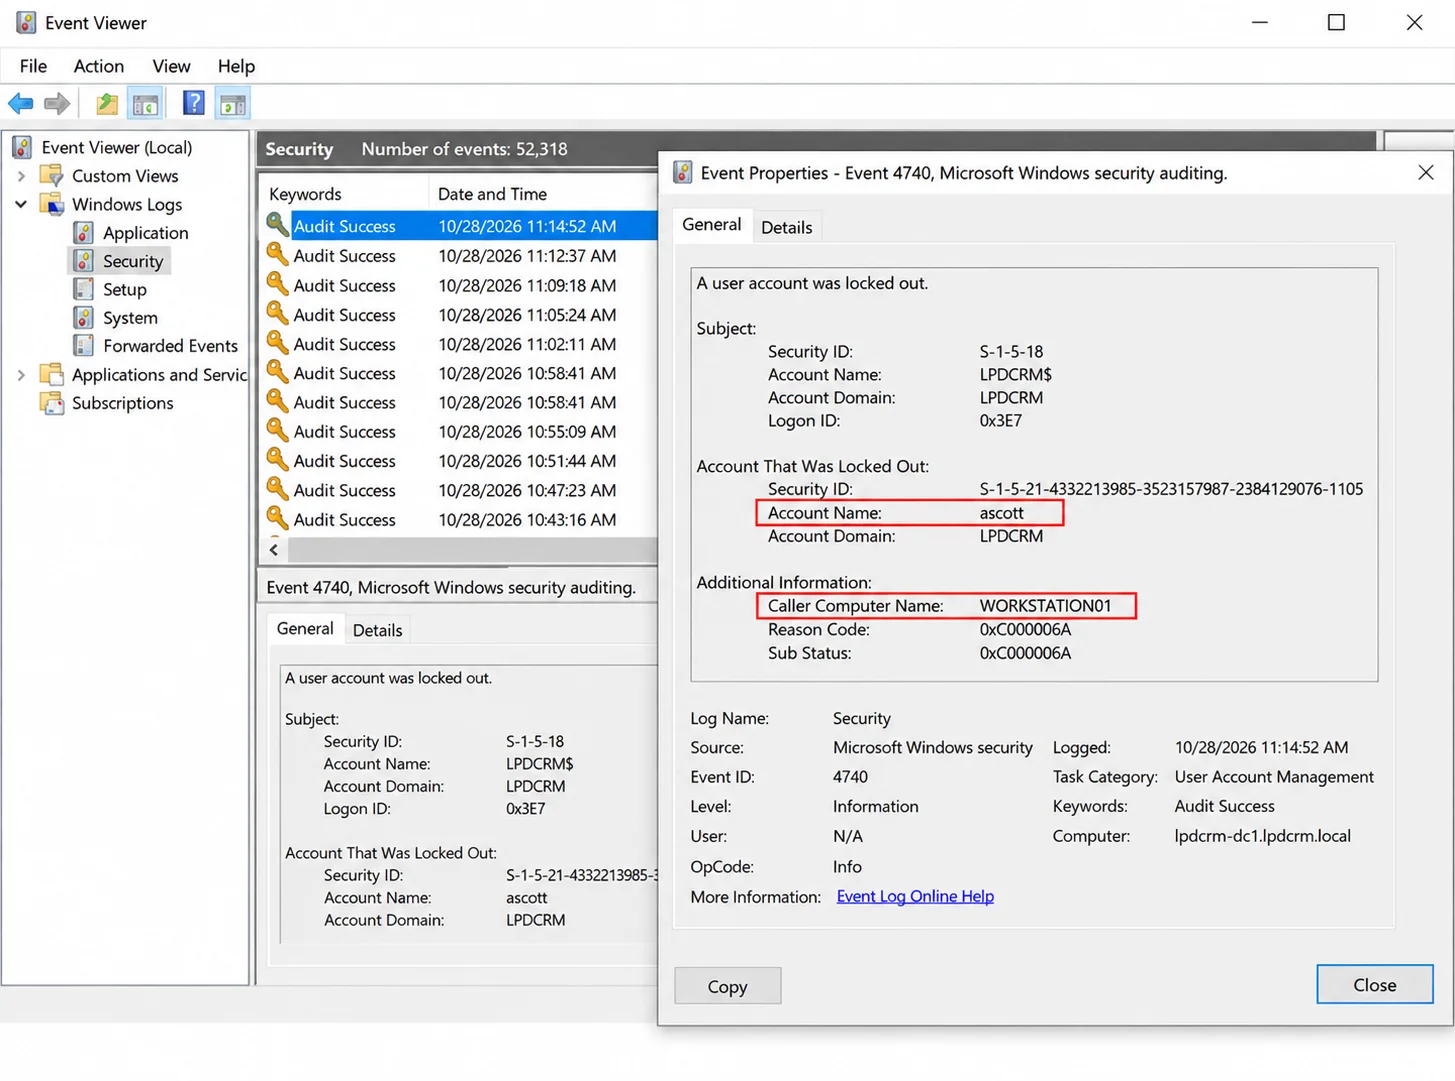
The Caller Computer Name field identifies the computer reported in the lockout event. This may indicate the source of the failed authentication attempts, but further investigation may be required to identify the actual device, service, or application responsible.
How to Find Out the Cause of Account Lockout?
To investigate the cause of an account lockout, examine related failed authentication events on the relevant domain controllers and, where necessary, the source computer.
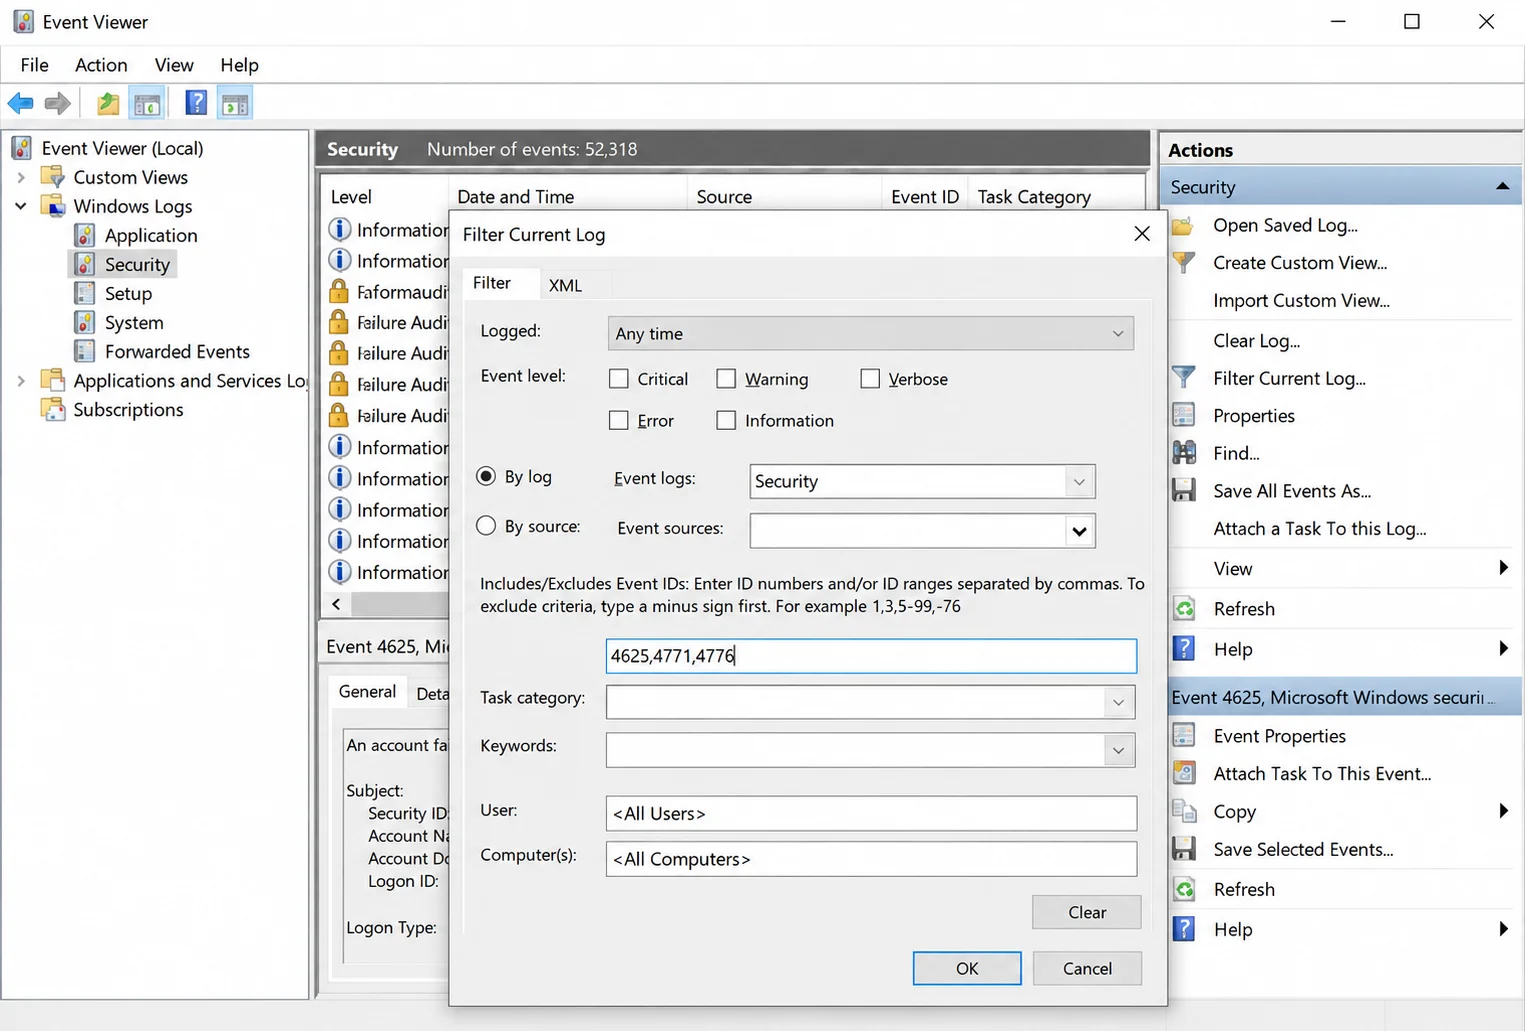
- In Event Viewer, check for Event ID 4625 (failed logon). Also review Event ID 4771 (Kerberos pre-authentication failure) and Event ID 4776 (NTLM credential validation) on the relevant domain controllers, depending on the authentication method.
- In the Actions pane, click Find, enter the locked-out account name, and click Find Next to locate related authentication events.
- Look for failed authentication events recorded immediately before and around the account lockout time. Open the relevant events to examine their details.
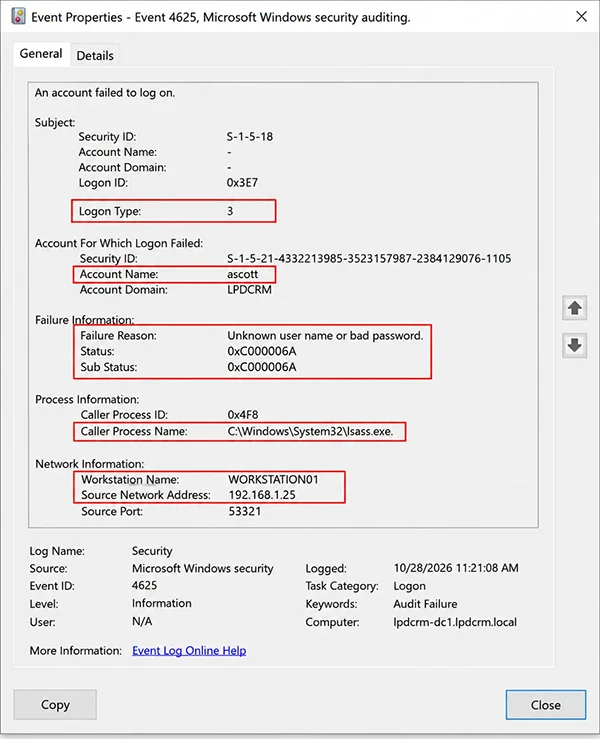
- Review the Logon Type, Failure Reason, Status, Sub Status, Workstation Name, and Source Network Address fields in Event ID 4625, where available. The Caller Process Name field may help identify the process involved on the computer that recorded the event. Correlate these details with Event IDs 4771 or 4776 and investigate the identified device, service, or application to determine the underlying cause.
Troubleshooting Tips
- If Event ID 4740 is missing: Verify that Audit User Account Management (Success) is enabled under Computer Configuration > Policies > Windows Settings > Security Settings > Advanced Audit Policy Configuration > Account Management. Also check the Security logs on other relevant domain controllers.
- If Caller Computer Name is blank or unknown: The originating device may not have been identified in the lockout event. Correlate Event IDs 4625, 4771, and 4776 with the lockout time and check relevant VPN, RADIUS, or application logs where applicable.
- If lockouts continue after password reset: Clear cached credentials in Windows Credential Manager and check for scheduled tasks or services using the old password.
How Lepide Account Lockout Examiner (Free Tool) Helps
Lepide Account Lockout Examiner Free Tool generates Account Lockout Reports where complete information about the event is displayed in a single row. When you right-click on any event, the context menu will give you the following options; “Unlock”, “Reset Password” and “Investigate”.
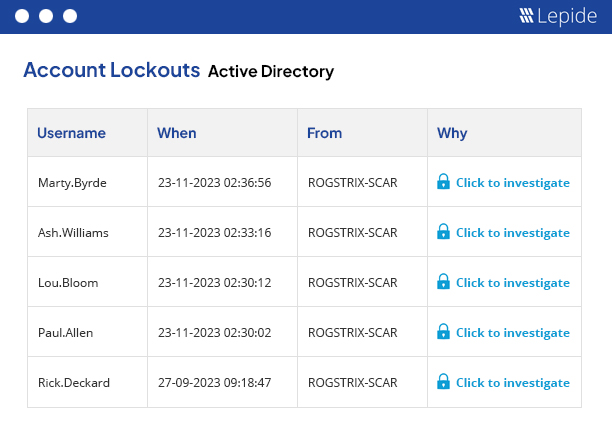
To run the Account Lockout Report:
- From the States & Behavior screen, expand the Active Directory component and click on Account Lockout Report
- Select a date range and click Generate Report
- The report is generated and can be grouped, filtered, saved and exported
Unlock Account
Click on this option to unlock the chosen user account. Once done, it shows the following message.
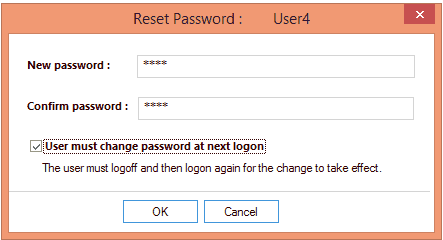
Reset Password
If you want to reset the users’ password, click on the “Reset Password” option. Enter the new password and then confirm it. Select the “User must change password at the next logon” option to force the user to change the password on the next logon.
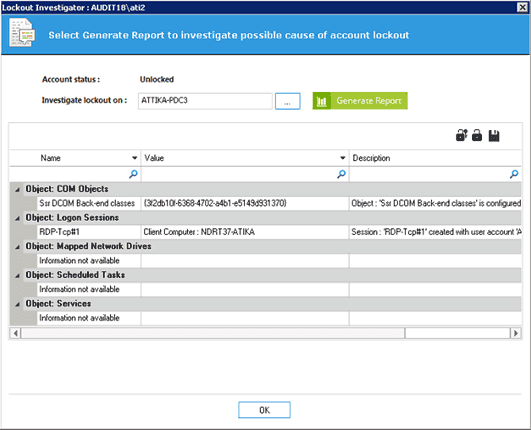
Investigate
In order to investigate how the user account was locked out click on the “Investigate” option in the context menu. After clicking on the “Investigate” button, “Lockout Investigator” window opens up. In this window, you can click on the “Generate Report” button to generate the report to view the reason behind the account lockout.
The Security Implications of Account Lockouts
Account lockouts are generally a harmless and completely common occurrence. Users forget their passwords frequently. A lot is often made of the operational effects of account lockouts, including downtime, disruption, and consumption of IT resources. However, account lockouts can be a symptom of something more sinister.
Often, if there are a large number of account lockouts over a very small period of time it can be an indication of a brute force attack, where attackers might be using password-spreading techniques to gain access to resources.
So, account lockouts are not to be brushed off completely. And it’s worth making sure that you have a way of knowing whether the account lockouts you’re seeing are normal everyday behavior for your employees or the symptom of something darker at work.
With Lepide, you can learn what the normal behavior for your employees looks like, and receive real-time alerts whenever behavior deviates from this norm. You can also deploy any number of pre-defined threat models to automatically detect and react to threats such as brute force attacks, or password spraying.
Frequently Asked Questions
Event ID 4740 records an Active Directory account lockout. The Caller Computer Name field may identify the computer associated with the lockout, but additional investigation may be required to confirm the actual source.
Check Event ID 4740 in the Security log on the PDC Emulator domain controller. The Caller Computer Name field may identify the source computer. If the information is missing or unclear, investigate related authentication events.
Event ID 4625 records failed Windows logon attempts. For Active Directory authentication failures, also check Event ID 4771 for Kerberos pre-authentication failures and Event ID 4776 for NTLM credential validation.
The PDC Emulator is the recommended starting point for investigating account lockouts. However, Event ID 4740 may also be recorded on other domain controllers involved in processing the lockout.